EU AI Act compliance, built into the platform.
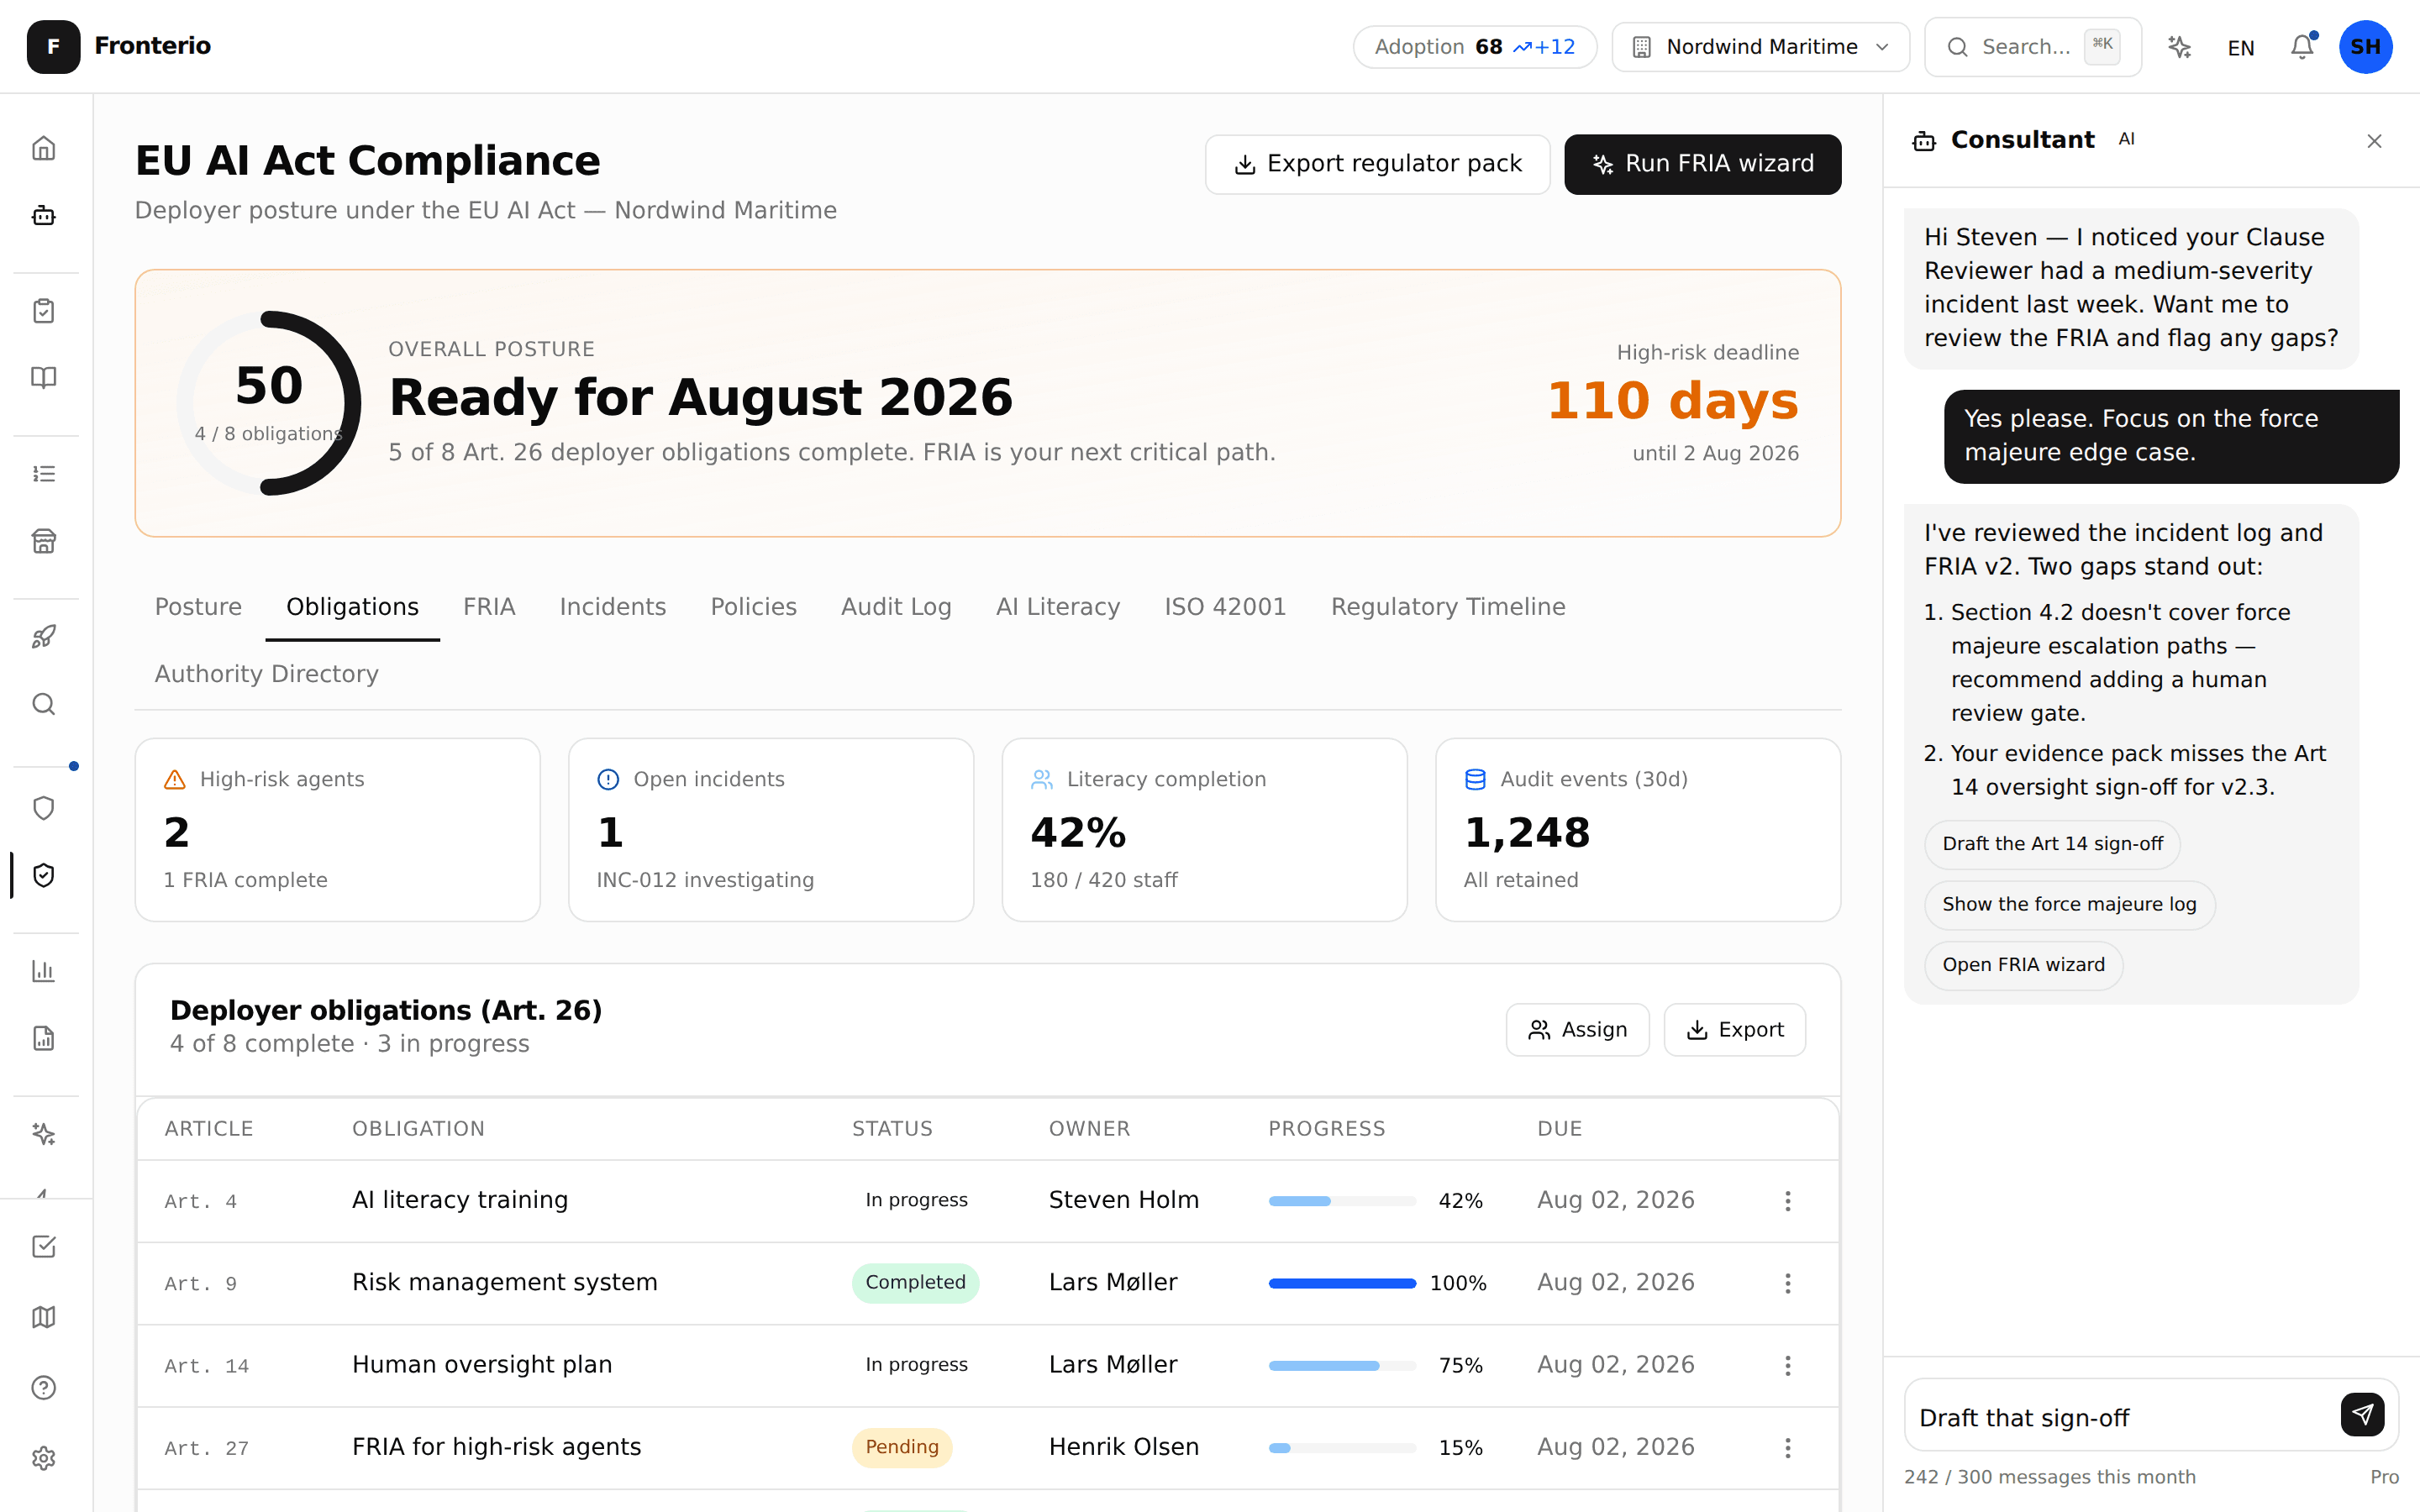
If you use AI tools, you are a deployer under the EU AI Act. Fronterio covers the deployer obligations in one place. Risk classification, the FRIA wizard, an immutable audit log and AI literacy records. The nightly Autopilot checks the evidence behind six of your thirteen tracked deployer obligations, tracks Article 73 timelines, and writes your operational monitoring reports.
Deployer obligations tracked, from human oversight to log retention
Risk tiers every AI system is classified into
Register that carries the evidence for all of it
You're a deployer: here's what that means
Most companies using AI are deployers, not providers. The EU AI Act draws a clear line: if you BUILD AI models, you're a provider. If you USE AI tools (Microsoft Copilot, ChatGPT, Claude, custom agents), you're a deployer. Either way, Fronterio covers the deployer obligations in one place.
Deployers face a specific set of obligations — Fronterio tracks 13 of them. Providers — companies building their own high-risk AI — face 13 more under Article 16. High-risk obligations apply from December 2027, which is time enough to get ready properly. And more immediately: regulators and enterprise customers already ask for proof of compliance during procurement.
The core deployer obligations Fronterio tracks
AI Literacy Training
Article 4: Ensure staff operating AI systems have sufficient AI literacy. Track who has been trained, when, and on what.
Human Oversight
Article 14: Maintain human oversight of high-risk AI systems. Document who oversees what, with what authority to intervene.
Operational Monitoring
Article 26(5): Monitor AI system operation for anomalies, risks, and incidents. Record observations systematically.
Fundamental Rights Impact Assessment
Article 27: Conduct FRIAs before deploying high-risk AI in HR, credit, insurance, or public services. Document affected groups and mitigations.
Transparency Disclosure
Article 50: Inform people when they interact with AI. Label AI-generated content clearly. No deceptive practices.
Incident Reporting
Article 73: Report serious incidents to authorities. Maintain an incident log with root cause analysis and corrective actions.
Log Retention
Article 26(6): Retain automatically generated logs from high-risk AI systems for the period required by the provider or at least 6 months.
Data Input Relevance
Article 26(4): Ensure data inputs to high-risk AI systems are relevant and representative for the intended purpose.
What only Fronterio does
Nightly Compliance Autopilot
Deterministic engine auto-checks the evidence behind 6 of your 13 tracked deployer obligations from platform data every night. Forward-only: never downgrades your manual progress.
Article 73 deadline clock
Serious-incident workflow starts the reporting clock when an incident is classified as serious and reminds the responsible owner as the deadline approaches. Competent authority directory seeded for all 30 EEA states.
Weekly Post-Market Monitoring
Weekly operational monitoring reports per high-risk agent (Article 26(5)), generated every Monday: usage volume, incident rate, human-override rate, complaint signal, drift alert. Regulator-ready PDF export.
Article 5 NLP detector
Before you register an agent, a deterministic pattern detector scans the description for 8 prohibited-practice signatures (emotion+workplace, social+scoring, biometric+real-time+public, predictive+policing, subliminal, vulnerability exploitation, facial scraping, biometric categorisation).
AI-drafted policies in 8 EU languages
Transparency (Art 50), FRIA (Art 27), Risk Management (Art 9) policy skeletons in your org language: English, Danish, Swedish, Norwegian, Finnish, German, Dutch, French. Edit, publish, done.
Third-party transparency auto-wire
Connect Microsoft 365 Copilot, Google Gemini, or Anthropic Claude, and Fronterio auto-drafts the Article 50 transparency disclosure in your org language, advances the obligation, and logs inference-location + transfer-mechanism (SCCs, EU-US DPF, Microsoft EU Data Boundary) to your audit log.
Technical documentation auto-generator (Art 11 / Annex IV)
Building your own high-risk AI? Fronterio auto-generates the full Annex IV technical documentation from your agent's configuration — system prompt, tool bindings, and guardrails snapshot — versioned per published agent version.
Hard-gated prohibited practices
Agents that match Article 5 prohibited practices are blocked at registration. The risk wizard cannot complete. No surprise unacceptable agents in production.
Audit records that cannot be rewritten
Article 12 requires tamper-evident record-keeping. Fronterio enforces it in the database itself: audit records can never be edited or deleted — by anyone, including us.
GPAI-downstream deployer support (Art 53)
Using GPT-4, Claude, or Gemini as the base for your agents? Model-type selector captures you as a GPAI-downstream deployer and reminds you to follow the provider instructions (Article 53).
ISO 42001 Certification Readiness Pack (Business+)
Going beyond EU AI Act? Fronterio auto-maps your governance data to all 38 ISO/IEC 42001 Annex A controls, generates a Statement of Applicability in one click, bundles a complete audit pack, and provides built-in management review + internal audit workflows. Work done for the EU AI Act gives your ISO 42001 readiness a head start from day one.
Why teams choose Fronterio
Fronterio automates what matters: the nightly evidence collection, the Article 73 deadline clock, the weekly operational monitoring reports (Article 26(5)), the NLP Article 5 detector, the auto-wired transparency disclosures when you connect Copilot or Gemini. This is infrastructure-grade compliance tooling, built by people who actually read the regulation.
How Fronterio gets you compliant
Take the free assessment
A 15-minute AI Readiness Assessment reveals your compliance gaps across 6 dimensions.
Classify your AI agents
Register every AI tool your company uses. Automatic EU AI Act risk classification: unacceptable, high, limited, or minimal.
Complete obligations
Guided workflows for each deployer obligation. Ask Fronterio helps draft FRIAs, oversight plans, and training programmes.
Export audit documentation
Board-ready PDF reports with your live compliance posture, agent registry, obligation status, and tamper-evident audit trail.
Manual compliance vs Fronterio
Without Fronterio
- Hire external consultants for a one-off report
- Manual spreadsheets for agent tracking
- 3-6 months to reach baseline compliance
- No ongoing monitoring or audit trail
- Risk classifications quickly go stale
With Fronterio
- Scoped to the organisation, not per user
- Automated agent registry with risk classification
- Baseline compliance in under 2 weeks
- Continuous monitoring + immutable audit log
- Ask Fronterio answers compliance questions 24/7
“The EU AI Act isn't about stopping AI adoption. It's about building trust. Companies that get compliance right early will have a competitive advantage in every enterprise procurement process.”
Based on EU Commission guidance on deployer obligations, 2025
Compliance built in, evidence that assembles itself
The AI Value Scan finds where AI creates value: a readiness assessment, a ranked value estimate, and one priced move. The compliance suite runs underneath it. Deeper still are the connected estate and the provider obligations under Article 16.
Get ready properly
Start free. See where AI creates value first, with the compliance floor ready when you deliver. No credit card.